Experts from ESET discovered 13 apps in the Google Play Store that steal Instagram users' login credentials for that very app. Everything indicates that the goal of the cybercriminals behind these malicious apps is to trade likes, comments, and follower counts on Instagram.
In the detected malicious apps found in Google Play, a threat detected by ESET as Android/Spy.Inazigram was hidden. By the time the apps detected by ESET were reported to Google, they had been downloaded by more than 1.5 million users in total. The threat actors lured their victims into downloading their apps by promising to increase the number of followers, likes, and comments on the user's Instagram profile.
All the detected apps used the same technique to steal login credentials – they displayed a fake Instagram login screen to the user. The data entered there was sent immediately to the cybercriminals' server, and the user was shown a message that they could not log in to the app because they had entered an incorrect password.
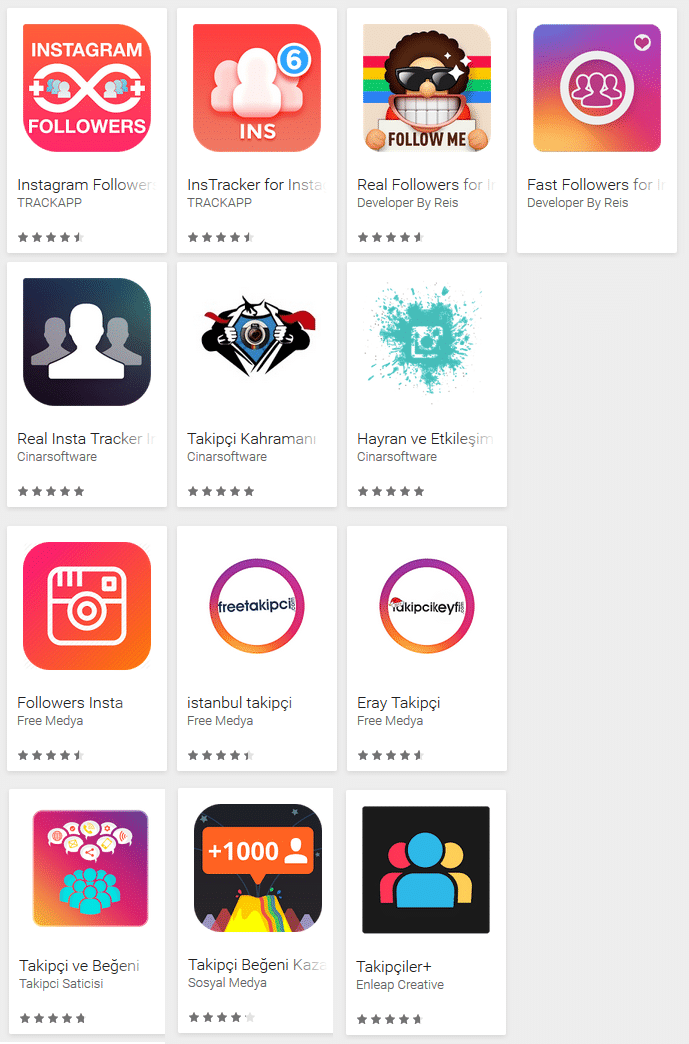 Everything indicates that when creating these threats, the cybercriminals based them on a business model whose main goal was selling new likes, comments, or new followers to other Instagram users. Profiles taken over by cybercriminals also make it possible to send spam messages or display ads. Not to mention the loss of privacy – by taking over an account, a fraudster gains access to the user's private photos and videos.